IT Governance Platforms Information With Policy Management, Auditing, and Reporting Details
IT Governance Platforms play an important role in helping organizations manage technology policies, cybersecurity responsibilities, internal controls, auditing activities, and regulatory requirements.
These platforms bring different governance activities together in one structured environment, allowing businesses to understand how technology decisions are made, who is responsible for them, and whether internal procedures are being followed.
The concept of IT governance developed as organizations became increasingly dependent on computer networks, digital records, enterprise applications, and information systems. As technology became connected to daily business operations, organizations needed consistent methods to manage information security, technology risks, regulatory responsibilities, and operational accountability.
Traditional governance activities often involved spreadsheets, paper documents, separate reporting systems, and manual approval procedures. Managing these activities across different departments could create inconsistent records and make it difficult to identify policy gaps. IT governance platforms emerged to organize these responsibilities through centralized digital management.
Modern platforms generally combine several functions, including:
Policy management for creating, reviewing, distributing, and updating internal policies.
Audit management for organizing assessments, collecting evidence, and tracking findings.
Risk management for identifying technology-related threats and evaluating their potential effects.
Compliance monitoring for checking organizational activities against applicable requirements.
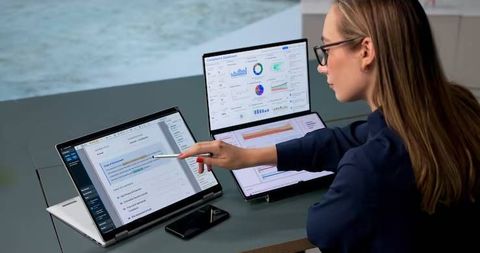
Reporting and analytics for presenting governance information through dashboards and structured reports.
These systems may operate independently or connect with enterprise applications, identity management systems, cybersecurity tools, and document management environments. Their main purpose is to create a consistent approach to technology oversight and organizational accountability.
Importance
IT governance platforms matter because technology decisions affect employees, customers, business partners, and the wider public. Organizations handle information such as customer records, payment details, employee information, business documents, and operational data. Weak governance can create problems involving unauthorized access, incomplete documentation, inconsistent procedures, and inadequate risk monitoring.
A structured governance environment helps organizations understand their responsibilities and maintain visibility over technology-related activities.
Who Uses IT Governance Platforms?
Different organizational groups use these platforms for different purposes.
IT departments: Monitor technology policies, infrastructure controls, access permissions, and operational procedures.
Compliance teams: Organize regulatory requirements, maintain documentation, and monitor compliance activities.
Internal auditors: Review controls, collect supporting evidence, record findings, and prepare audit reports.
Risk management teams: Identify potential threats and monitor corrective measures.
Senior management: Review governance performance, outstanding risks, and organizational responsibilities.
Employees: Access internal policies, complete acknowledgments, and understand applicable workplace procedures.
Problems Addressed by Governance Systems
Without centralized governance, organizations may experience duplicated documentation, unclear responsibilities, outdated policies, and delayed audit preparation. Different departments may also follow inconsistent procedures when handling sensitive information.
IT governance platforms address these challenges through centralized records, approval workflows, responsibility assignments, and reporting functions.
For example, when an organization updates its information security policy, the platform can maintain the revised document, record approval details, identify employees who need to acknowledge it, and retain information about previous versions.
Main Organizational Benefits
Common operational benefits include:
Improved visibility into technology policies and internal controls.
More organized audit documentation and evidence collection.
Consistent policy approval and revision procedures.
Clearer responsibility assignments across departments.
Better tracking of identified risks and corrective activities.
More structured reporting for management reviews.
These capabilities support informed decision-making, although their effectiveness depends on accurate information, appropriate configuration, and regular organizational oversight.
Recent Updates
IT governance platforms have continued evolving alongside developments in cybersecurity, artificial intelligence, regulatory compliance, and enterprise technology management.
A noticeable trend from 2024 through 2026 is the movement toward integrated governance environments. Organizations increasingly prefer systems that connect policy management, risk monitoring, audit activities, and compliance reporting rather than maintaining completely separate applications.
Artificial Intelligence in Governance
Artificial intelligence is becoming more common in governance-related workflows. Some platforms incorporate automated document classification, policy analysis, evidence organization, and reporting assistance.
AI-supported capabilities can help identify potentially missing information or highlight differences between internal policies and selected compliance requirements. However, automated findings require human review because AI systems can misunderstand context or produce inaccurate interpretations.
Continuous Compliance Monitoring
Traditional audits often focus on specific review periods. Newer governance approaches increasingly emphasize continuous monitoring, allowing organizations to review selected controls throughout normal operations.
This approach can help identify changes in access permissions, incomplete approvals, policy exceptions, and other control-related issues between formal audits.
Integration With Enterprise Systems
Modern platforms increasingly connect with cloud applications, cybersecurity monitoring systems, identity management tools, and enterprise resource planning environments.
Integration helps reduce repeated data entry and creates a more connected view of organizational risks. Data accuracy, integration permissions, and system compatibility remain important considerations.
Important Technology Governance Developments
| Development | Governance relevance |
|---|---|
| AI governance | Documentation and oversight of AI-related risks |
| Cloud governance | Monitoring cloud access, configurations, and controls |
| Automated auditing | Organizing evidence and identifying control gaps |
| Continuous monitoring | Reviewing controls throughout operations |
| Integrated reporting | Combining information from different departments |
| Data privacy management | Monitoring information handling and access procedures |
Overall, the current direction emphasizes automation, connected reporting, AI accountability, and more frequent assessments of organizational controls.
Laws or Policies
IT governance platforms are influenced by different legal frameworks, regulatory requirements, and recognized technology management standards. The exact requirements depend on the organization's location, industry, activities, and the type of information it handles.
There is no single worldwide law that governs every IT governance platform. Instead, organizations may need to consider several overlapping frameworks.
International Governance Standards
ISO/IEC 27001 is an internationally recognized information security management standard. It provides a framework for establishing, implementing, maintaining, and continually improving an information security management system.
COBIT is another widely recognized framework that helps organizations organize enterprise IT governance and management activities. It addresses areas such as accountability, performance measurement, risk management, and technology alignment with organizational objectives.
NIST Cybersecurity Framework 2.0 also provides guidance for managing cybersecurity risks. Its updated structure includes a dedicated Govern function, emphasizing organizational responsibilities, policies, oversight, and risk strategy.
Regional Regulatory Requirements
Different jurisdictions have introduced regulations affecting information governance, cybersecurity, privacy, and digital accountability.
Examples include:
General Data Protection Regulation (GDPR): Establishes personal data protection requirements for organizations within its scope, including responsibilities involving information handling, security, and accountability.
NIS2 Directive: Establishes cybersecurity risk management and incident reporting requirements for covered entities within the European Union.
Digital Operational Resilience Act (DORA): Establishes digital operational resilience requirements for covered financial entities in the European Union.
EU AI Act: Introduces risk-based requirements for certain artificial intelligence systems, including governance, transparency, and oversight obligations.
These frameworks have different scopes and applicability conditions. An organization should determine which requirements apply to its operations rather than assuming that every regulation applies universally.
Internal Governance Policies
Organizations also establish internal rules to guide everyday technology activities. Common examples include:
Information security policies.
Data retention and protection policies.
Employee access management policies.
Incident response procedures.
Third-party technology risk policies.
Software usage and approval guidelines.
IT governance platforms help maintain these documents, record approvals, track revisions, and organize evidence demonstrating how internal procedures are implemented.
Tools and Resources
Several categories of tools and established frameworks support IT governance, policy management, auditing, and reporting activities. Organizations generally select them according to their operational requirements, regulatory responsibilities, technology environments, and internal capabilities.
IT Governance and GRC Platforms
Governance, Risk, and Compliance (GRC) platforms provide centralized environments for managing policies, risks, audits, and compliance activities.
Examples include ServiceNow Integrated Risk Management, IBM OpenPages, Archer, and MetricStream. Their capabilities vary, but common functions include workflow management, control tracking, audit documentation, and management reporting.
Policy Management Tools
Policy management systems organize internal documents throughout their lifecycle.
Important capabilities include version control, approval tracking, document distribution, acknowledgment records, and scheduled policy reviews. These features help organizations maintain consistent documentation and identify outdated policies.
Audit Management Software
Audit management tools help organize internal and external assessment activities. They may include audit planning, evidence repositories, control testing, finding management, and corrective action tracking.
These capabilities help auditors maintain structured records and communicate assessment results to relevant departments.
Reporting and Analytics Tools
Reporting applications convert governance information into understandable summaries. Dashboards may display audit progress, outstanding findings, compliance status, risk classifications, and policy review activities.
Power BI, Tableau, and reporting modules within enterprise GRC platforms are examples of technologies used to present organizational information.
Important Evaluation Considerations
When assessing IT governance platforms, organizations generally examine:
Policy management and document control capabilities.
Audit planning and evidence management.
Risk assessment and compliance monitoring.
Reporting flexibility and dashboard configuration.
Integration with existing enterprise applications.
User permissions and information protection.
Data retention and audit history.
Scalability and administrative requirements.
Selecting appropriate tools requires understanding organizational processes and the specific governance responsibilities involved. Software alone cannot replace internal accountability, qualified oversight, or effective management procedures.
FAQs
What Are IT Governance Platforms?
IT governance platforms are digital systems that help organizations manage technology policies, internal controls, audits, risks, and compliance activities. They centralize documentation and provide structured reporting for organizational oversight.
How Does Policy Management Software Work?
Policy management software organizes the creation, approval, distribution, revision, and acknowledgment of organizational policies. It maintains document histories and helps track whether relevant employees have reviewed updated procedures.
What Is the Difference Between IT Governance and GRC Platforms?
IT governance focuses on directing and overseeing technology activities to support organizational objectives. GRC platforms combine governance, risk management, and compliance functions within a coordinated management environment.
How Do IT Governance Platforms Support Auditing?
They help organize audit schedules, maintain evidence records, assign responsibilities, document control assessments, and track corrective actions. Reporting functions also help auditors communicate findings to management.
Which Standards Are Relevant to IT Governance?
Commonly referenced frameworks and standards include ISO/IEC 27001, COBIT, and NIST Cybersecurity Framework 2.0. Applicable regulations may also include GDPR, NIS2, DORA, and the EU AI Act, depending on organizational activities and jurisdiction.
Conclusion
IT governance platforms provide structured environments for managing technology policies, auditing, risk assessments, and compliance reporting. Their capabilities are increasingly connected with artificial intelligence, cloud systems, and continuous monitoring processes. International standards and regional regulations influence how organizations establish and maintain their governance responsibilities. Effective implementation depends on suitable technology, accurate documentation, clear accountability, and ongoing human oversight.